Understand your
security risks.Know what to do next.
Senior AI security and offensive security advisory to help technology teams identify exposure, prioritize remediation, and make informed decisions.
AI Security
Assessments & advisory
Offensive Security
Red team strategy
Threat Intelligence
Adversary informed
Program Strategy
Executive clarity
AI Security Assessment & Roadmap
Choose this custom assessment when you need deeper document review and advisory for your AI application's data flows, permissions, and integrations, with a tailored roadmap. Unlike the fixed price AI Security Quick Review, scope, deliverables, pricing, and dates are agreed for your project.
Once AI features are in production, it is rarely clear what data is exposed, which permissions those systems hold, how they can be abused, and what the integrations actually reach.
A prioritized view of your AI security risks and a practical improvement plan your team can act on.
- Executive summary
- Risk scenarios specific to your application
- Prioritized recommendations
Defined after an initial conversation, so the engagement matches what you actually have.
This engagement covers document review and advisory. Practical technical testing is a separate activity that requires an agreed scope and written authorization. It does not certify systems or guarantee the absence of vulnerabilities.
Cybersecurity services for modern businesses.
Focused security reviews designed to identify risks, prioritize action, and give your team clear next steps. Each one is an initial review of limited scope.
Web & API Security Review
Up to 1 web app and 3 critical API endpoints
Web apps, APIs, portals, and platforms used by customers.
External Attack Surface Review
Up to 3 domains and 25 public assets
Companies that need visibility into their exposure on the internet.
Cloud Security Quick Review
Up to 1 cloud account, subscription, or project
AWS, Azure, or GCP environments needing a fast risk review.
AI Security Quick Review
Up to 1 AI application, workflow, chatbot, copilot, or LLM integration
An initial risk review and next steps for one AI use case, with limited scope and a fixed price. For greater depth and a tailored roadmap, choose the custom assessment.
Cybersecurity Risk Snapshot
Up to 1 business unit, product, or small environment
Founders, CTOs, and executives needing security clarity.
Executive Advisory Session
1 session, 1 primary topic
One focused cybersecurity, AI Security, or leadership question.
Packages are designed for focused initial review and prioritization. Larger scopes, additional assets, practical testing, implementation, and ongoing advisory are quoted separately.
All prices are listed in USD.
Larger scopes, built around your program.
For needs that require greater depth, we design a project with a tailored scope and deliverables.
Discuss your projectPricing for custom projects is quoted after an initial conversation.
A senior cybersecurity lab and advisory practice.
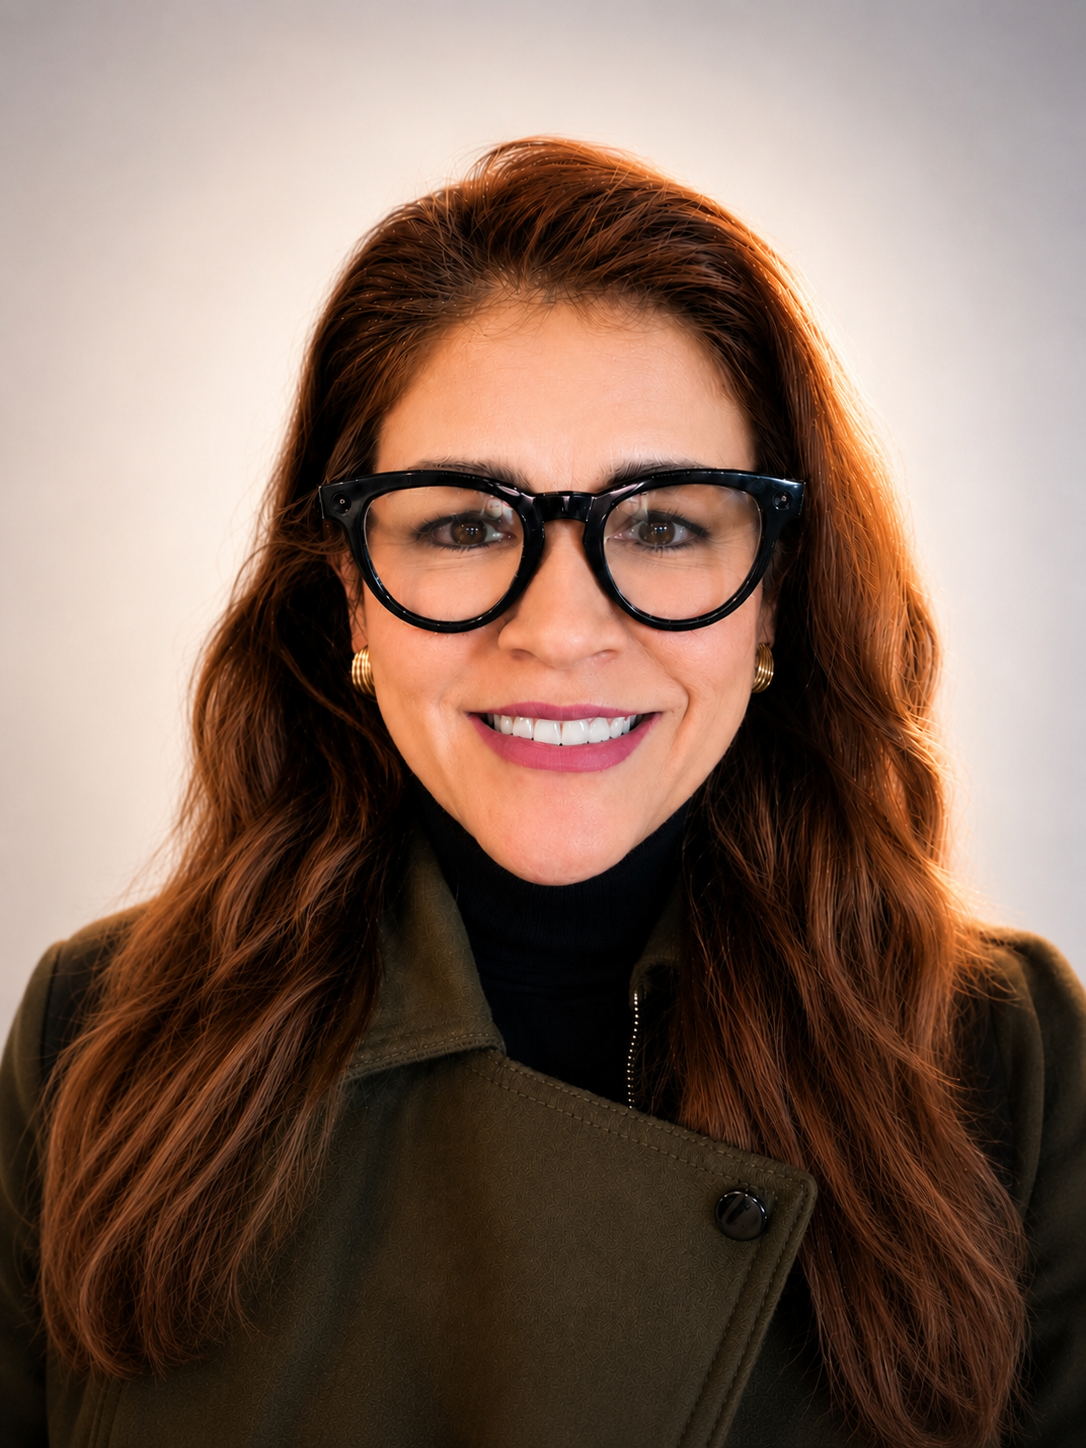
Gema Landaverde is the founder of BlackGem Labs, a cybersecurity leader with global experience across FICO, AB InBev, Deloitte, Colgate-Palmolive, and others. Her expertise spans offensive security, red team operations, threat intelligence, threat hunting, AI security, and cybersecurity compliance.
She helps security and technology leaders identify critical exposures, assess AI security risks, strengthen security programs, and address compliance requirements. Her approach connects technical findings with business priorities, giving teams clear recommendations on what to address first and why.
Strategic depth. Technical conviction.
Built for the teams shaping modern technology.
A clear path from first conversation to results.
We understand your environment, what you need to protect, and the decision you are trying to make.
You receive a written scope, deliverables, price, and timeline before any work starts.
We review documents, architecture, or configurations within the agreed scope and keep you updated.
We walk your team through the findings and the prioritized actions that follow.
Field notes on security & AI.
May 9, 2026
5 AI Security Frameworks Every Leader Should Know
AI adoption is moving faster than most security programs can mature. For leaders building, integrating, or governing AI-enabled systems, it is no longer enough to understand “AI risk” at a high level. The next phase requires knowing the frameworks that help teams assess, test, and govern these systems safely.
Read more
February 7, 2025
Introducción al Pentesting Cloud con CloudGoat
Esta guía está orientada al acompañamiento del taller "Introducción al Pentesting Cloud con CloudGoat" , donde se muestran los fundamentos esenciales para realizar pruebas de seguridad en entornos cloud, utilizando AWS y herramientas como Terraform para la automatización de…
Read more
November 12, 2024
10-Day Plan for Learning Malware Development in C: Day 10 – Evasion Techniques and Feature Enhancements
Let's work on refining and improving the malware we’ve built over the past nine days. Specifically, we'll explore advanced evasion techniques that make detection by antivirus and security software more difficult, and we'll also add new features to extend the capabilities of our…
Read moreBlackgem Sentinel AI
Sentinel AI is being designed to help organizations manage AI application security risk with clarity, structure, and repeatability, from initial assessment through remediation and retesting.
Let's talk about your security strategy.
AI security, offensive security, or broader cybersecurity strategy: write to us and we will use the first conversation to confirm your needs and the right scope.